A structured path to ISO 27001, NIS2 & DORA readiness.
Audit-ready artifacts in weeks, not months.
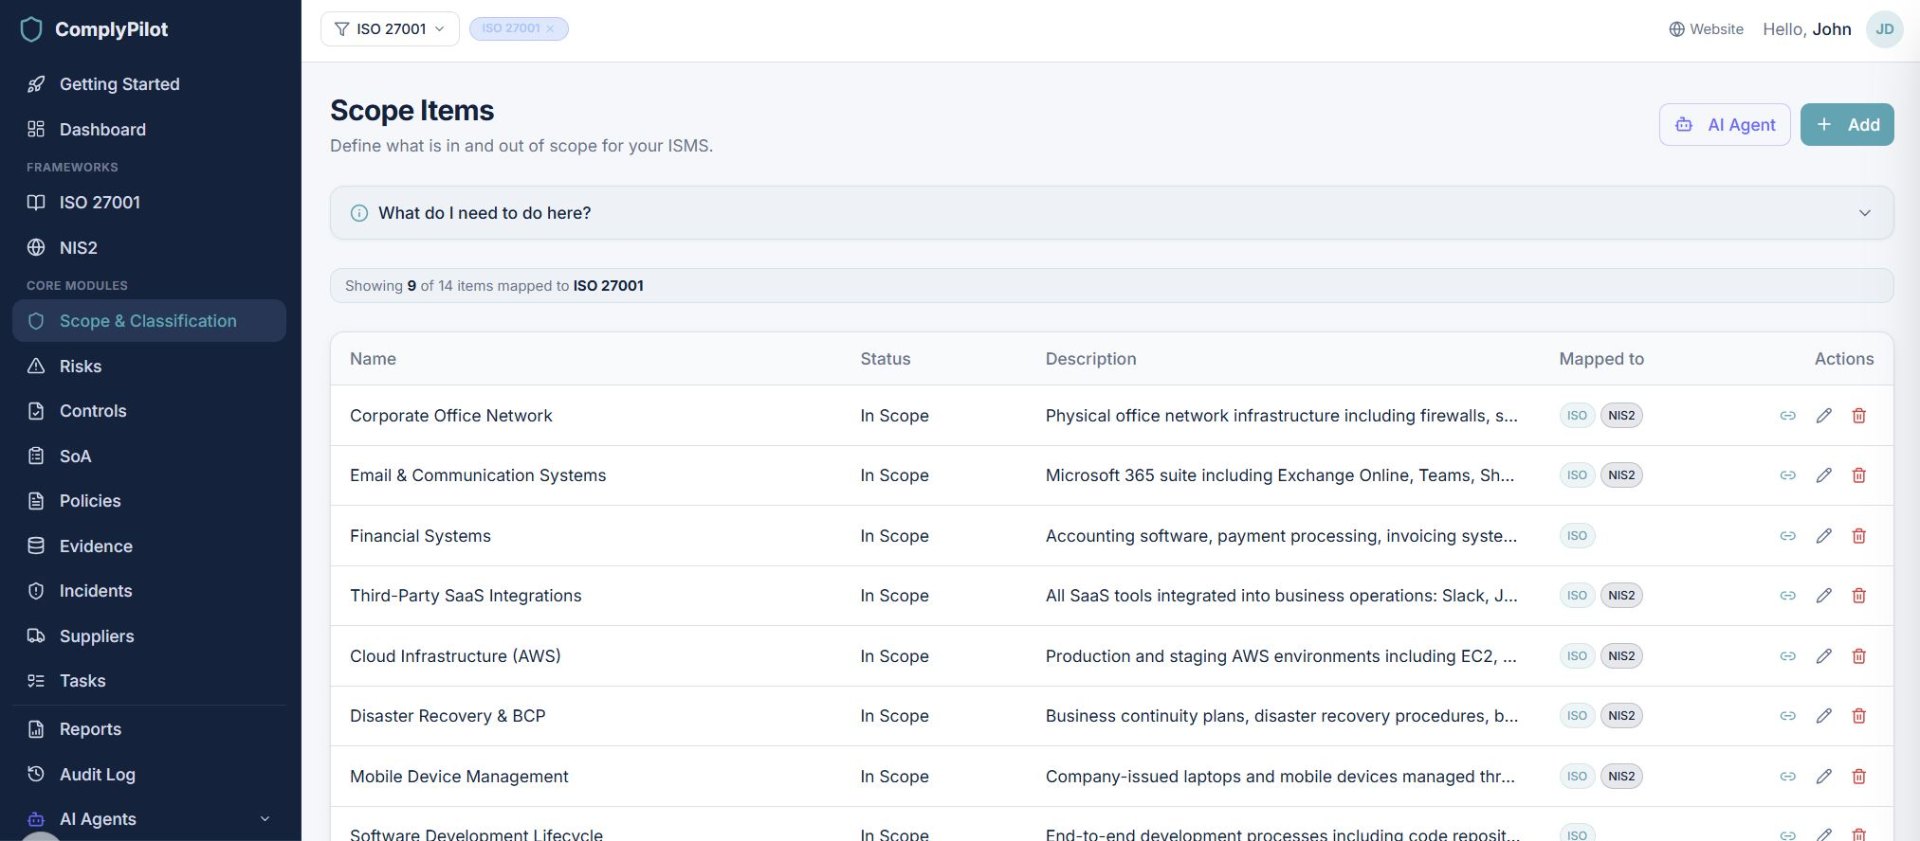
Scope Builder
Define what is in and out of scope for your ISMS. List assets, systems, and processes — from cloud infrastructure to third-party integrations — with clear statuses and descriptions.
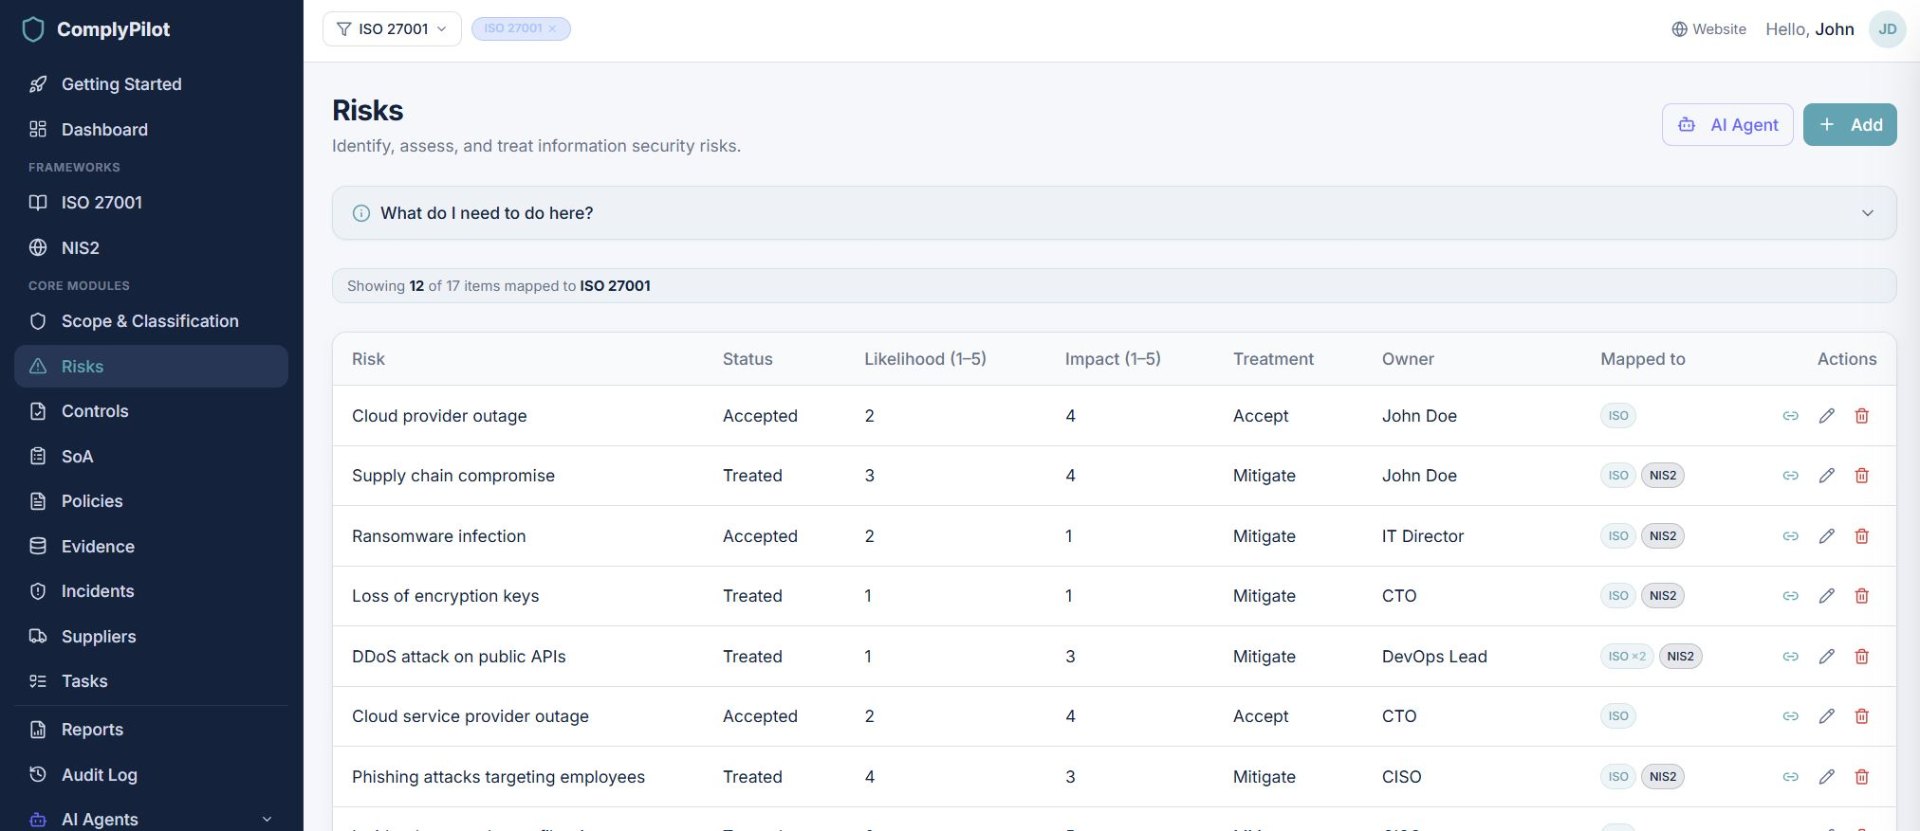
Risk Register
Identify, assess, and treat information security risks. Set likelihood and impact scores, assign owners, choose treatment strategies, and track each risk from identification through to acceptance.
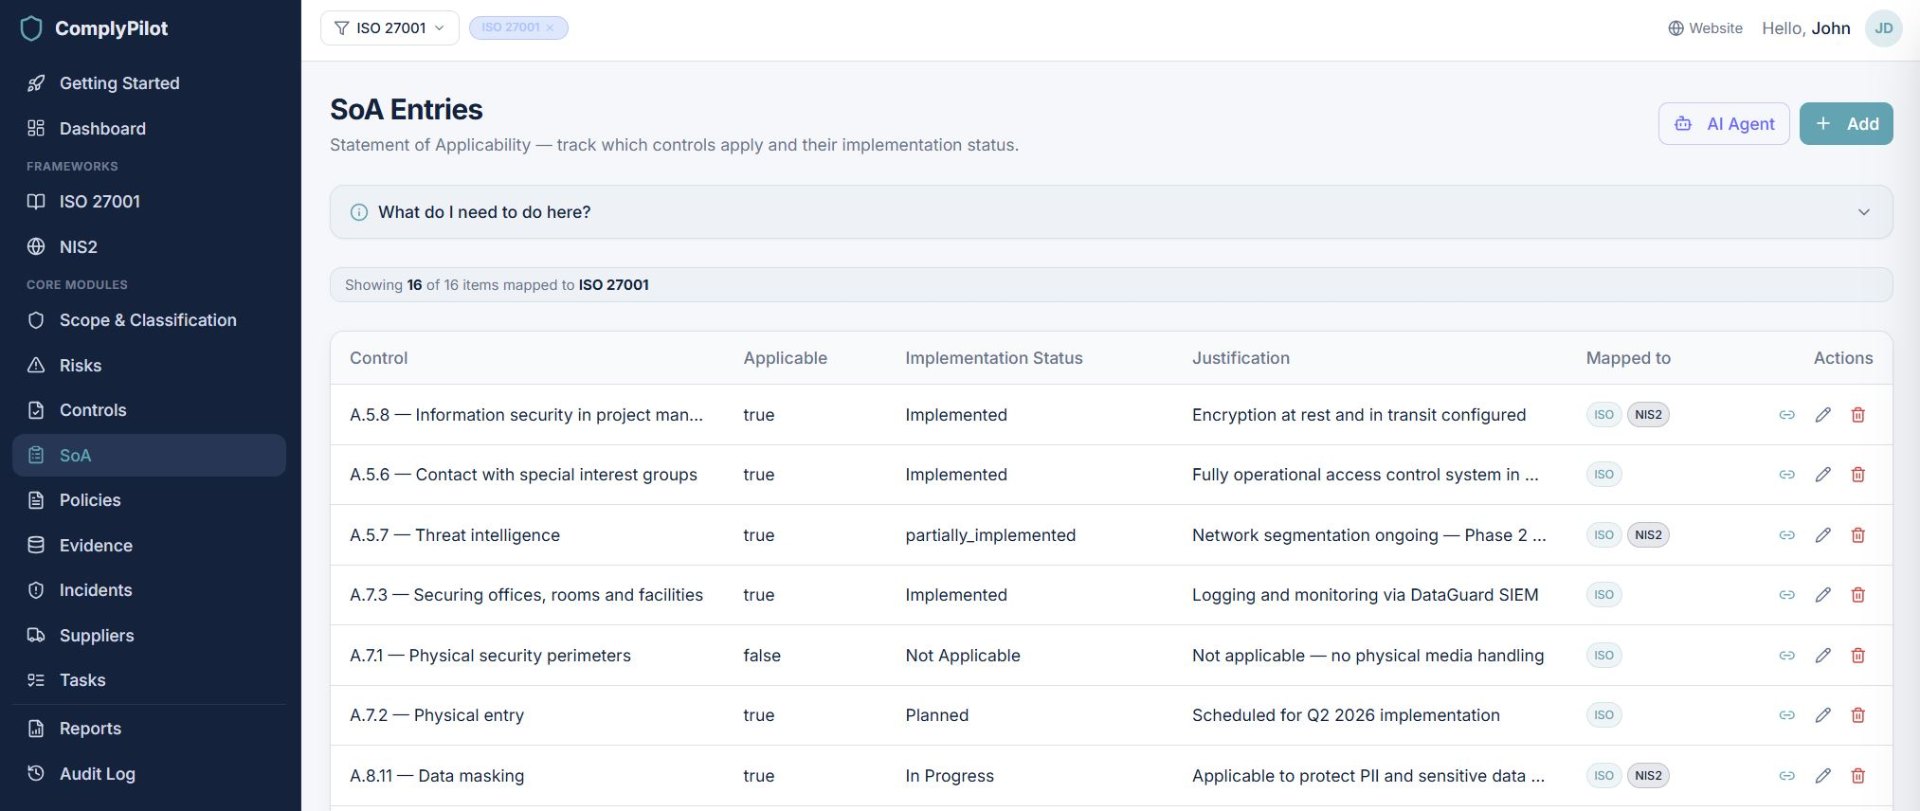
Statement of Applicability
Document every Annex A control with its applicability, implementation status, and justification. The SoA is the most-reviewed document during an ISO 27001 audit — keep it audit-ready at all times.
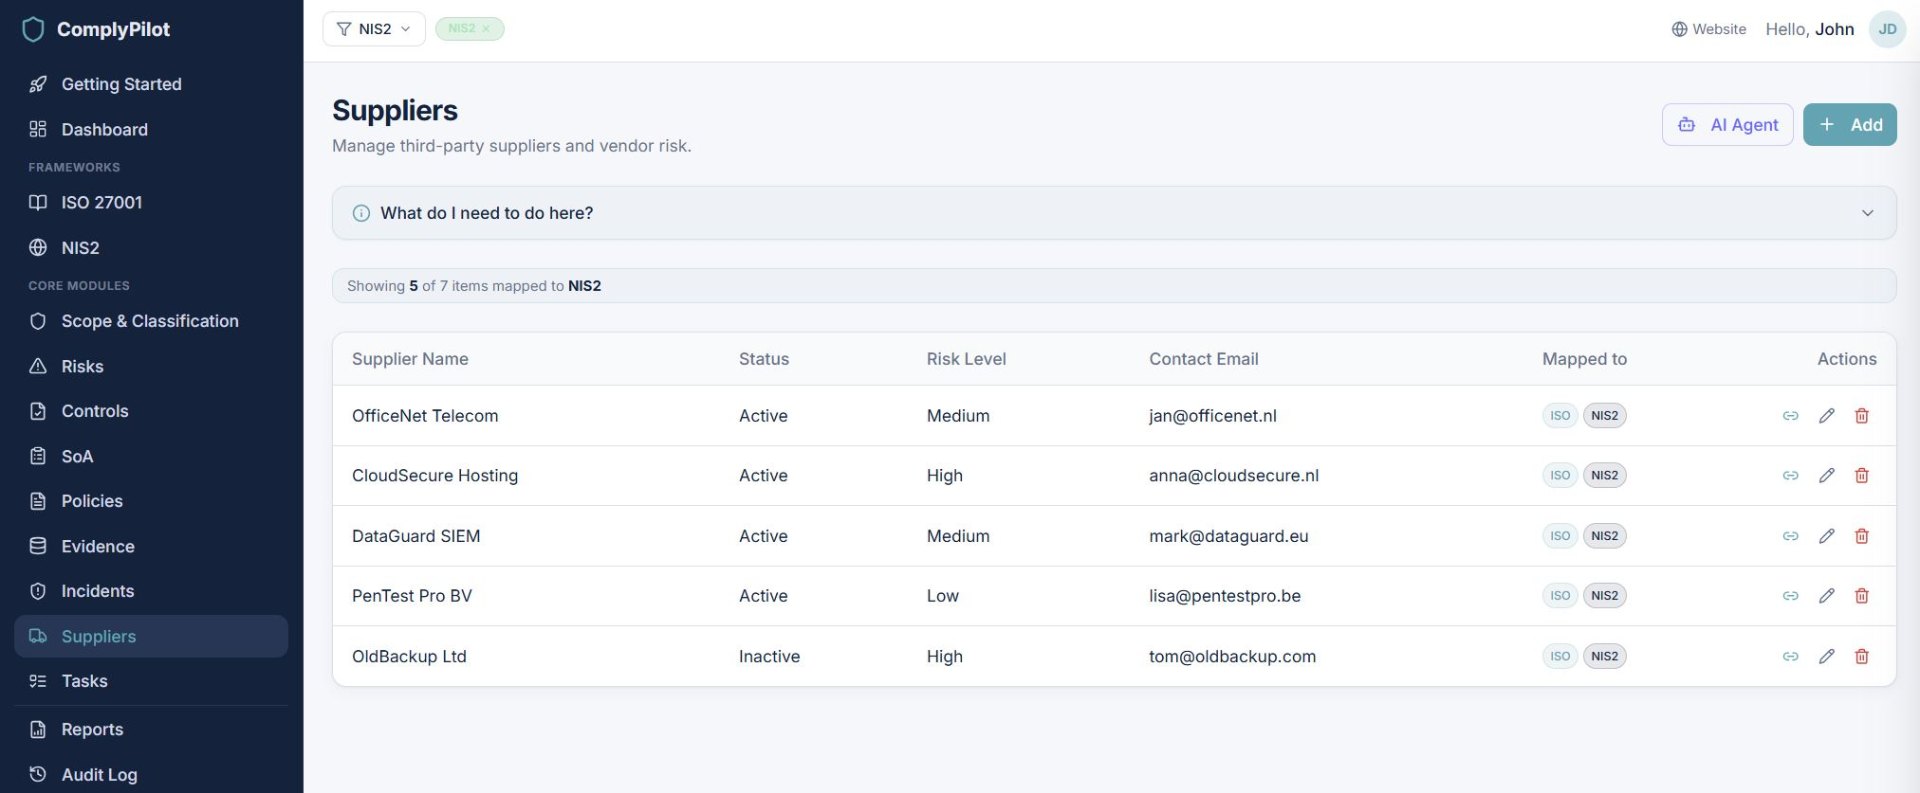
Supplier Management
Register and assess all third-party suppliers. Track risk levels, contact details, and compliance status. Link suppliers to framework requirements to prove supply-chain security to auditors and regulators.
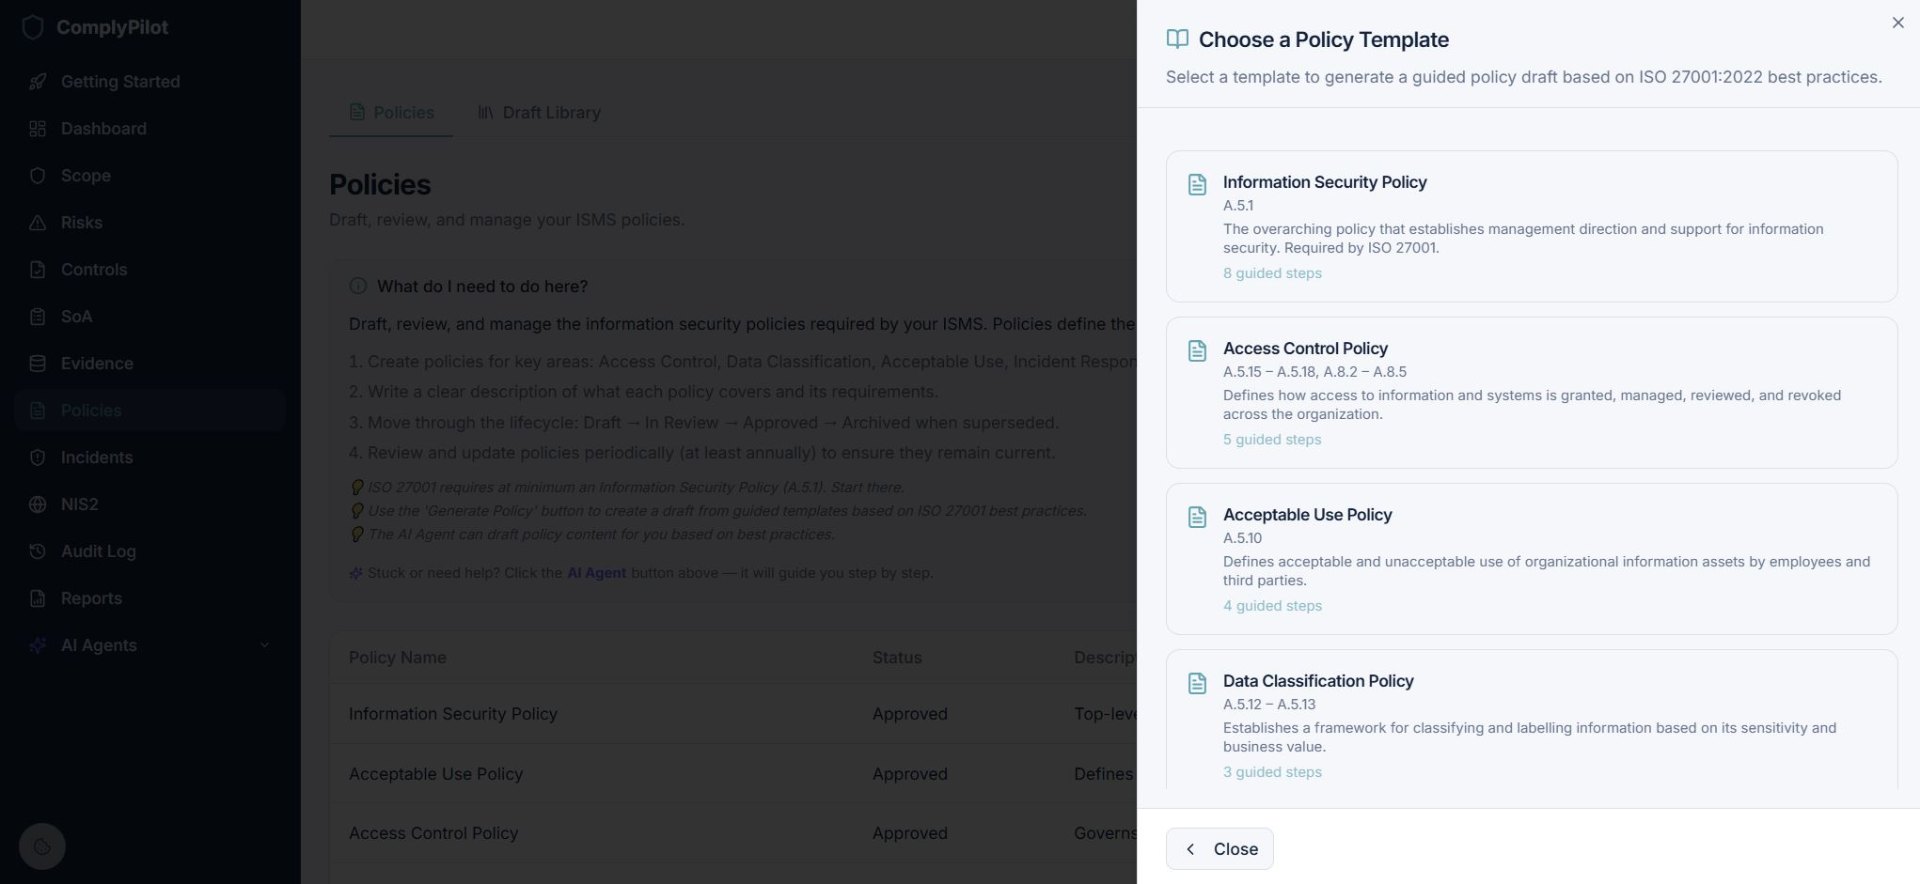
Policy Manager & Generator
Draft, review, and manage your ISMS policies. Choose from guided templates based on ISO 27001:2022 best practices, generate complete policy drafts, and maintain version control with change summaries.
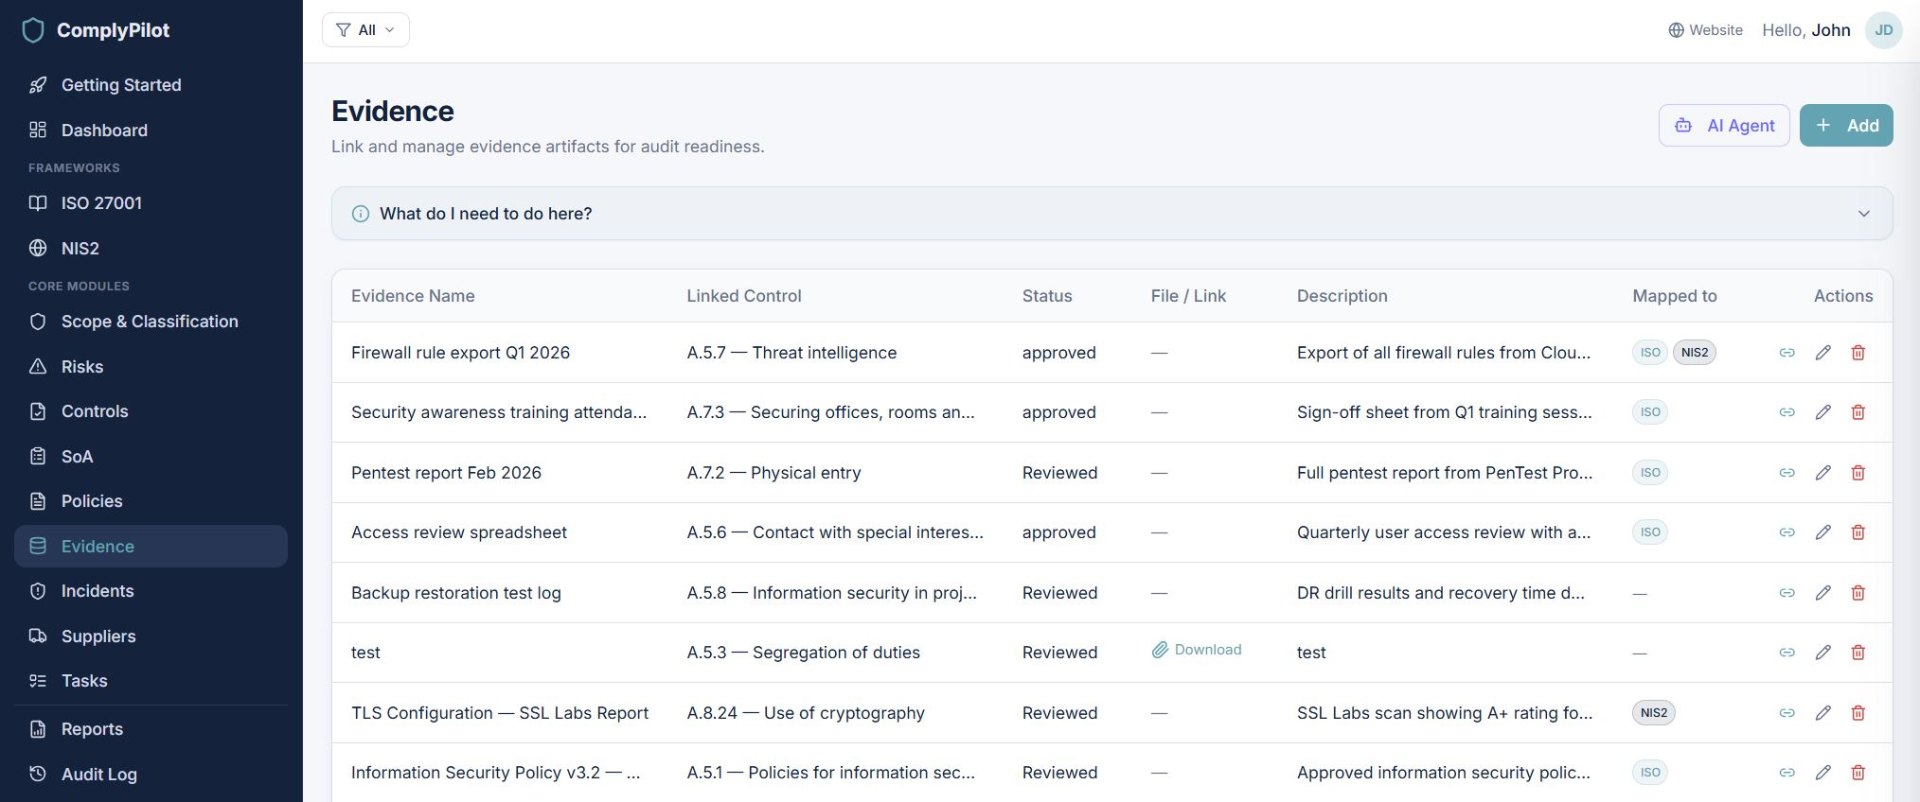
Evidence Vault
Collect, organise, and link evidence artifacts to controls and framework requirements. Track approval status, upload files, and ensure every audit question is backed by documented proof — ready when the auditor asks.
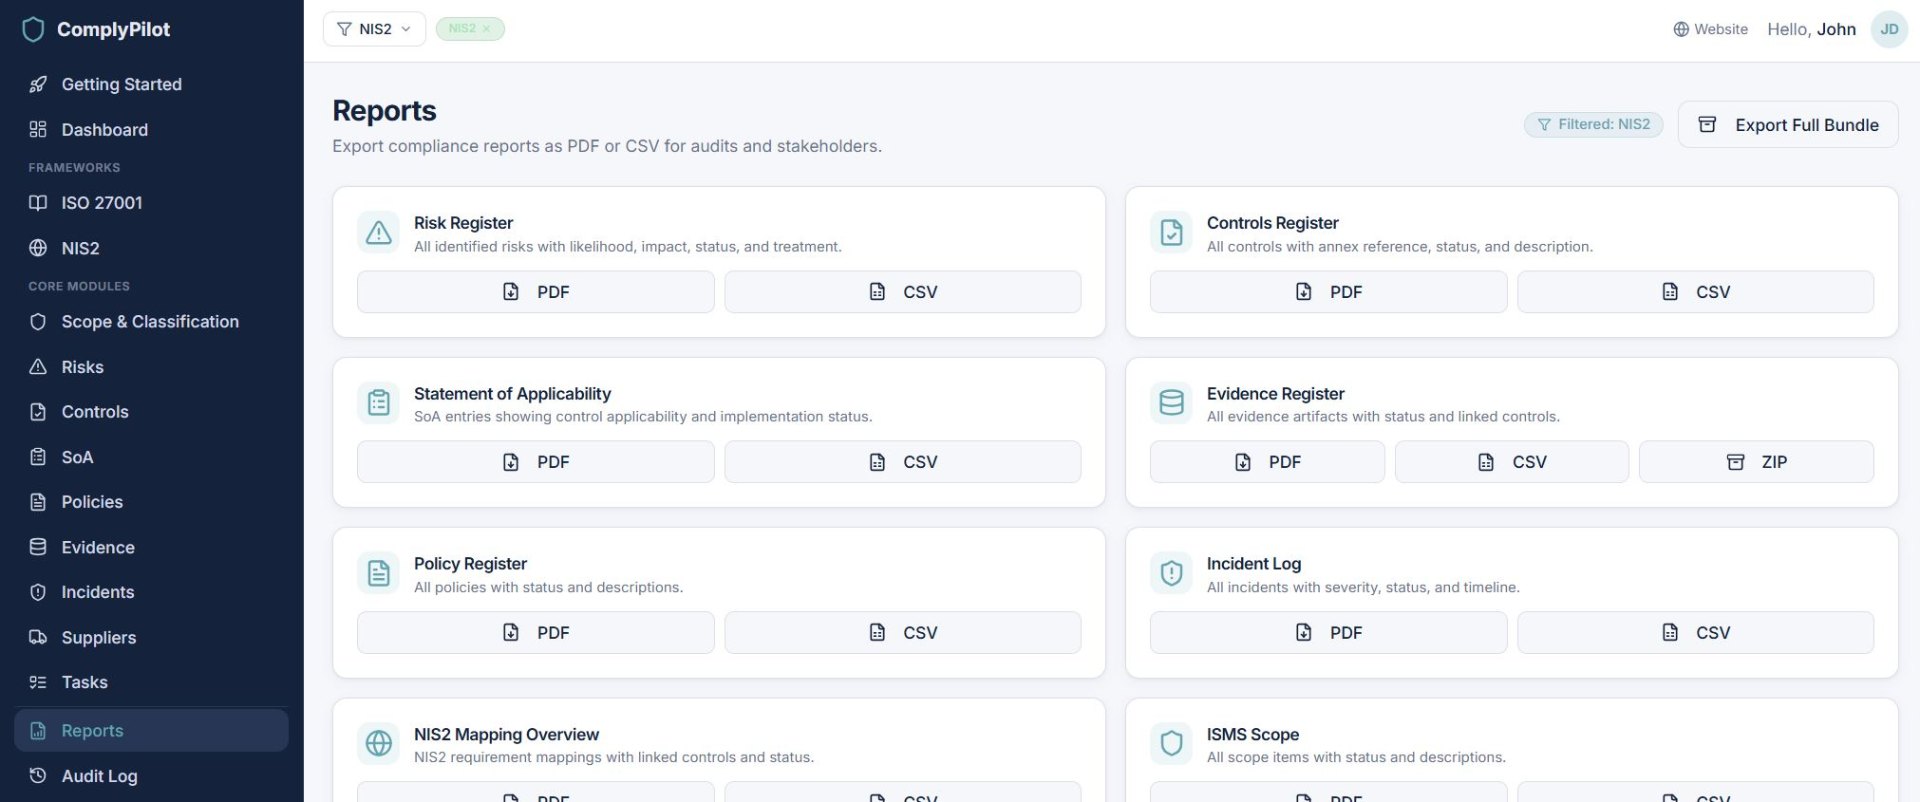
Reports & Exports
Export compliance reports as PDF or CSV for audits and stakeholders. Generate risk registers, controls registers, SoA documents, evidence logs, policy registers, incident logs, and more — all in one place.
AI Agents
Context-aware AI agents that draft policies, suggest risk treatments, auto-generate SoA entries, and coach you through incidents. Every suggestion requires your explicit approval before saving.
AI-assisted — all suggestions require approval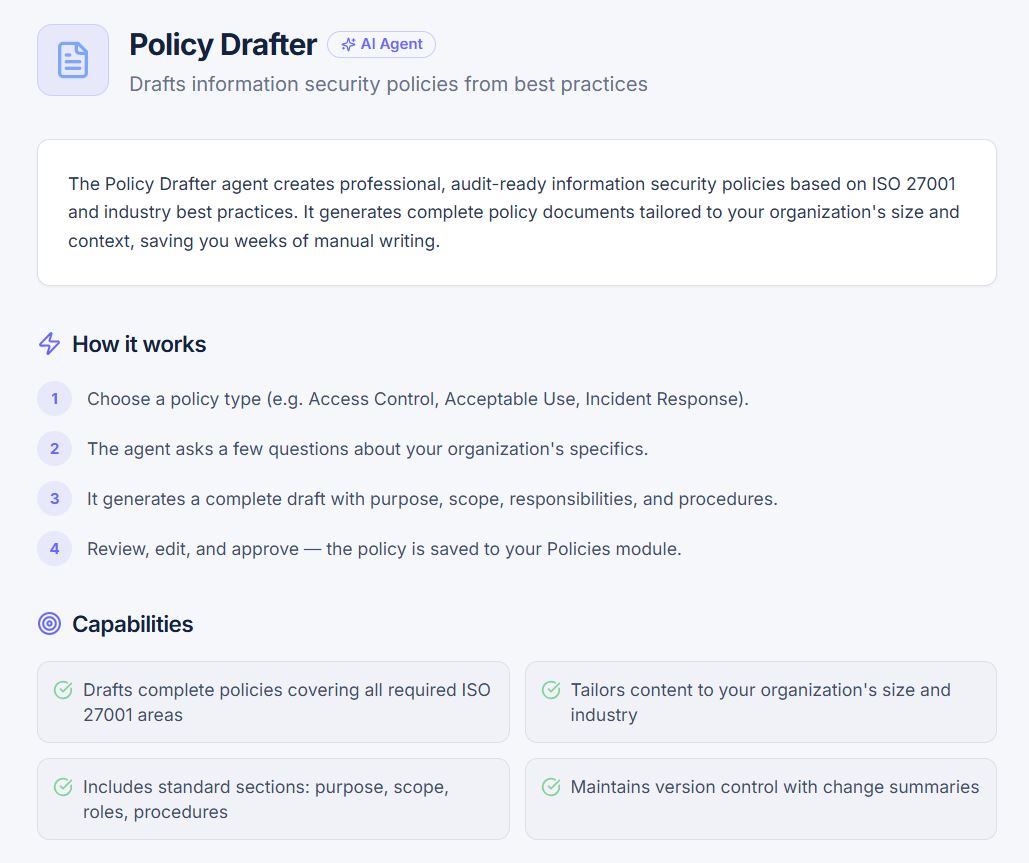
…and much more
Controls management, evidence vault, incident tracking, audit logs, team collaboration, and continuous improvement — everything you need for a complete ISMS, all in one platform.