NIS2 Directive Compliance
Navigate EU cybersecurity obligations with structured clarity — from entity classification to incident reporting readiness.
Track NIS2 readiness by category
ComplyPilot maps your compliance posture across all NIS2 requirement categories — governance, risk management, incident reporting, supply chain, and more — into a single visual dashboard.
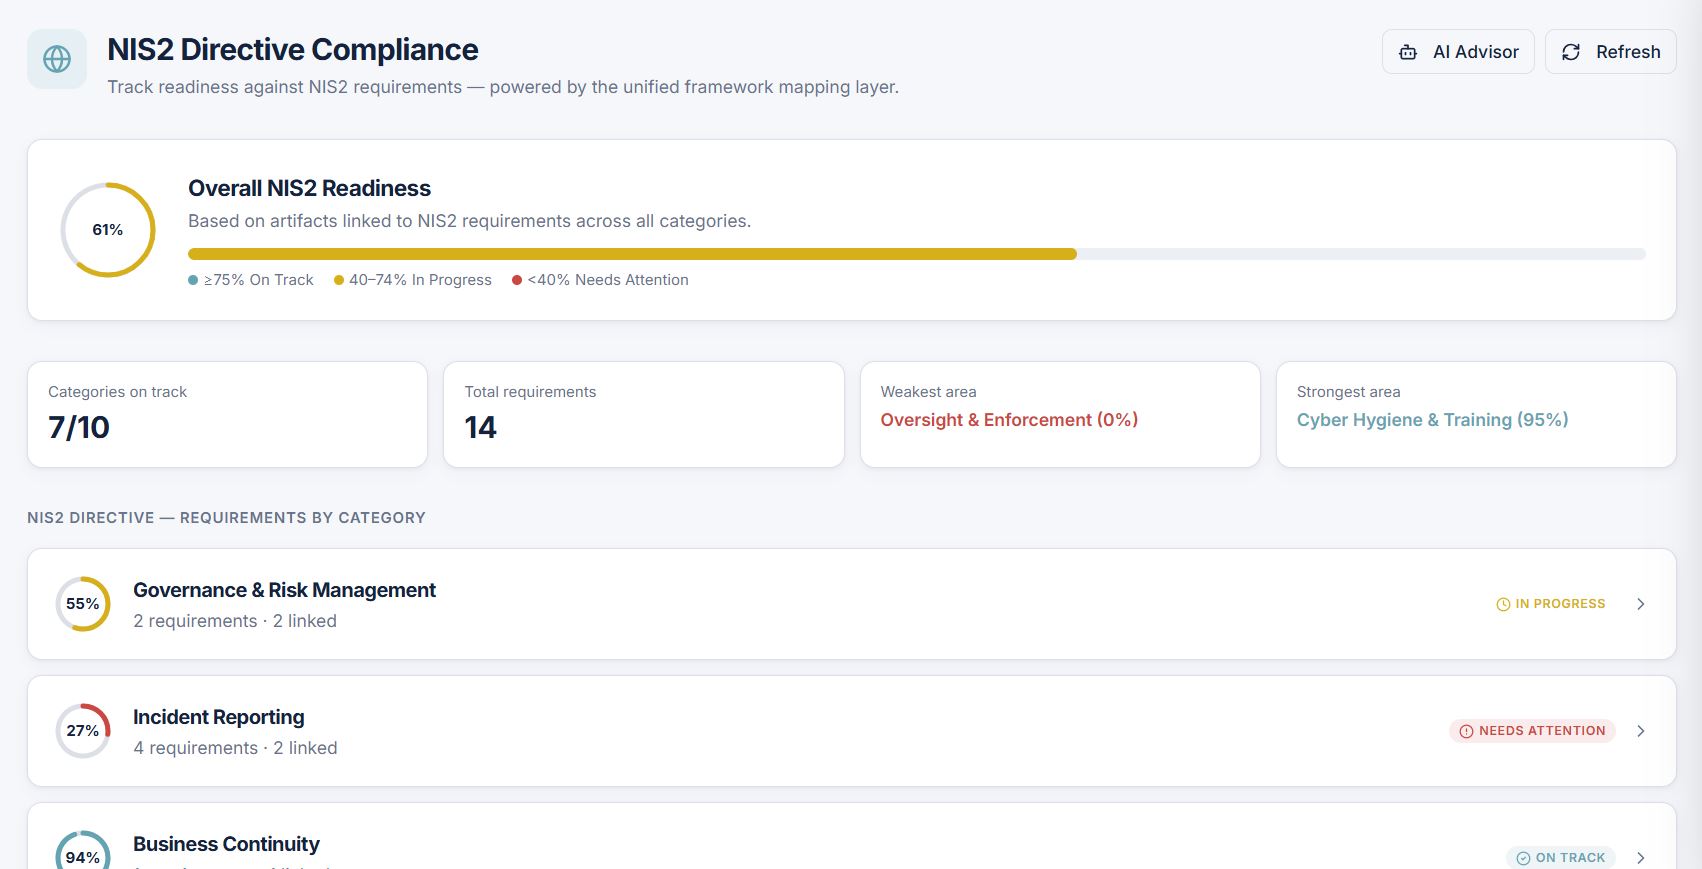
≥75% On Track
Category meets readiness threshold
40–74% In Progress
Work underway, needs completion
<40% Needs Attention
Critical gaps to address first
Structured support for every NIS2 obligation
Each capability maps directly to NIS2 directive requirements, helping you demonstrate compliance across all key areas.
Entity Classification
Determine whether your organization is classified as essential or important under NIS2. ComplyPilot helps you understand your obligations based on sector, size, and criticality.
Governance & Accountability
NIS2 mandates management accountability for cybersecurity. Structure your governance framework with clear responsibilities, policies, and board-level risk oversight.
Incident Reporting
Meet the multi-stage incident reporting timeline — from early warning within 24 hours to final reports within one month. ComplyPilot provides structured incident drafting and tracking.
Supply Chain Security
Assess and document third-party risks across your supply chain. Track supplier security postures and ensure contractual cybersecurity requirements are in place.
ISO 27001 Mapping
Leverage your existing ISO 27001 controls to address NIS2 requirements. ComplyPilot maps the overlap, helping you avoid duplicated effort and demonstrate compliance efficiently.
Cryptography & Access Control
Document your encryption policies, key management procedures, and access control mechanisms — demonstrating technical measures required under NIS2 Article 21.
Business Continuity
Structure your continuity and disaster recovery plans to meet NIS2 resilience requirements. Track backup strategies, recovery objectives, and crisis management procedures.
Cross-Border Coordination
Understand reporting obligations to national CSIRTs and competent authorities. ComplyPilot helps you prepare the required notifications for cross-border incidents.
Who does NIS2 apply to?
NIS2 classifies organizations into two categories based on sector, size, and criticality. Each category faces different levels of supervisory scrutiny and enforcement.
Essential Entities
Subject to proactive supervisory measures including on-site inspections, regular audits, and security scans. Must implement all cybersecurity risk-management measures comprehensively.
Sectors include
Energy, transport & water
Health & digital infrastructure
Banking & financial markets
Public administration & space
Important Entities
Subject to reactive supervision triggered by evidence of non-compliance. Same obligations apply but enforcement is proportionate to risk exposure and entity size.
Sectors include
Manufacturing & chemicals
Food production & distribution
Digital providers & postal services
Waste management & research
AI agents accelerate your NIS2 readiness
ComplyPilot's built-in AI agents can auto-map ISO 27001 controls to NIS2 requirements, draft incident notifications, assess supply chain risks, and coach you through governance frameworks — saving hours of manual compliance work.
Disclaimer: ComplyPilot provides structured support for NIS2 readiness. Final legal interpretation and compliance responsibility remains with the organization. Consult legal counsel for binding interpretations.