ISO 27001 Readiness
Structure your Information Security Management System with confidence — from scope definition to audit-ready evidence.
See your ISMS readiness at a glance
ComplyPilot calculates your overall ISO 27001 readiness in real time — aggregating completion data across scope, risks, controls, SoA, evidence, policies, and incidents into a single executive dashboard.
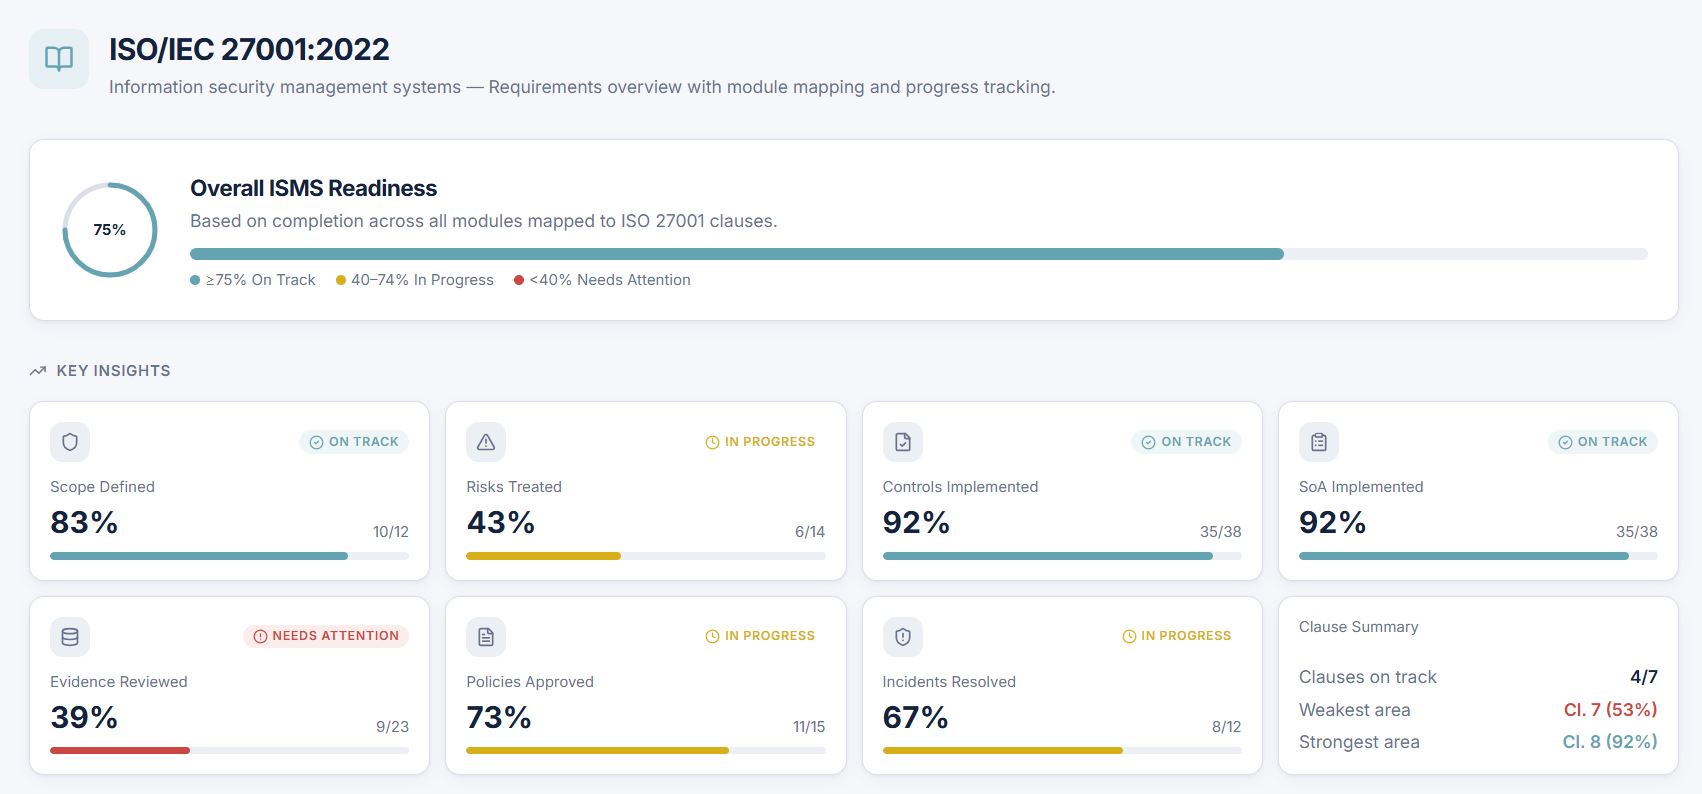
≥75% On Track
Module meets readiness threshold
40–74% In Progress
Work underway, needs completion
<40% Needs Attention
Critical gaps to address first
Everything you need for ISO 27001
Each module maps directly to ISO 27001 clauses and Annex A controls, giving auditors exactly what they expect.
Scope & Context
Define the boundaries of your ISMS — assets, processes, locations, and interested parties. ComplyPilot ensures nothing falls through the cracks when auditors ask about your scope statement.
Risk Register
Identify, assess, and treat information security risks with a practical methodology. Link each risk to Annex A controls and define treatment plans with clear ownership and timelines.
Controls & Annex A
Track all 93 ISO 27001:2022 Annex A controls with implementation status indicators. See at a glance which controls are implemented, in progress, or still need attention.
Statement of Applicability
Generate your SoA with clear justifications for every control. Track inclusion rationale and link evidence — the most-reviewed document during any ISO 27001 audit.
Evidence Library
Maintain structured evidence linked directly to controls and risks. Upload documents, screenshots, and logs — all organized and version-tracked for audit readiness.
Policy Generator
Draft ISO-aligned security policies using AI assistance. Maintain version history, track approvals, and ensure every policy stays current and audit-ready.
Incident Management
Log, track, and resolve security incidents with severity classification. Demonstrate to auditors that your organization has a mature incident response process.
Executive Reports
Generate board-ready compliance reports with readiness scores, risk heatmaps, and gap analysis — giving management the visibility they need without the complexity.
Let the AI Agent do the heavy lifting
ComplyPilot's built-in AI agents can auto-generate SoA entries from your existing controls, draft risk treatment plans, suggest policy content, and coach you through incident responses — saving hours of manual compliance work.
Note: ComplyPilot helps generate and structure ISO 27001 artifacts but does not guarantee certification. Certification is granted by accredited certification bodies following a formal audit.